Van Truong Tran

Information Security Engineer building accountable Autonomous SecOps workflows.

Autonomous SecOps connects signals, AI reasoning, human approval, and continuous validation.

Ho Chi Minh City, Vietnam

Onsite or hybrid full-time in Vietnam; remote for relevant international freelance work.

Autonomous Security Loop

  1. Signal Intake

    Collect security signals and the evidence needed to assess them.

  2. AI Reasoning

    Use evidence-grounded AI workflows to organize context for review.

  3. Human Approval

    Keep accountable human review at the decision point.

  4. Orchestration

    Coordinate approved security actions across repeatable workflows.

  5. Security Controls

    Apply and assess preventive and detective controls in practice.

  6. Continuous Validation

    Use controlled validation to improve future signals and safeguards.

  • Signal IntakeAI Reasoning: Signals gain evidence-grounded context.
  • AI ReasoningHuman Approval: AI-supported context reaches accountable review.
  • Human ApprovalOrchestration: Approved decisions initiate coordinated actions.
  • OrchestrationSecurity Controls: Coordinated work applies security controls.
  • Security ControlsContinuous Validation: Control behavior enters continuous validation.
  • Continuous ValidationSignal Intake: Validation outcomes improve incoming signals.

Experience

Security Operations Engineer InternTrusting SocialMay 2026 — Present

Ho Chi Minh City, Vietnam; onsite

Security operations work spanning control validation, evidence-led investigation, and endpoint detection.

  • Contributed to Zero Trust and DLP control validation.
  • Worked on automated threat-intelligence ingestion and evidence-grounded enrichment.
  • Supported intel-first hunting and macOS and Jamf detection engineering.
Security Researcher InternUniversity of Information TechnologyJun 2025 — Oct 2025

Offensive-security research focused on structured, human-reviewed penetration-testing workflows.

  • Researched LLM-assisted multi-stage penetration-testing workflows.
  • Covered reconnaissance, vulnerability discovery, and exploitation research.

Field records / threat-informed work

Operational Evidence

Zero Trust & DLP Control ValidationExperience validating security controls against expected behavior.project
  • Evaluated Zero Trust and data-loss-prevention control behavior.
  • Contributed evidence collection and review-ready observations.
  • Policy-path validation and controlled security testing.
  • Supported clearer decisions about control behavior.
security-operationszero-trustdlp
Autonomous Signal OperationsExperience building repeatable workflows for analyst-ready security signals.project
  • Developed automated signal intake, normalization, and enrichment workflows.
  • Contributed normalization, provenance checks, and human review steps.
  • Scheduled ingestion, structured normalization, and evidence-grounded enrichment.
  • Supported more consistent preparation of security information.
signal-intakeautomation
Evidence-led Investigation DesignExperience structuring focused investigation from approved evidence.research
  • Translated approved evidence into scoped investigation questions.
  • Connected evidence, hypotheses, and analyst validation.
  • Evidence-led hypothesis development and review.
  • Supported more focused investigation paths.
investigationevidence
macOS & Jamf Detection EngineeringExperience developing reviewable endpoint detection logic.project
  • Worked with macOS telemetry and Jamf-oriented detection engineering.
  • Contributed behavior analysis and detection review.
  • Endpoint telemetry analysis and detection-as-code practices.
  • Supported maintainable endpoint visibility.
detection-engineeringendpoint
LLM-assisted Multi-stage Pentesting ResearchResearch into structured LLM assistance across penetration-testing stages.research
  • Explored LLM-assisted reconnaissance, vulnerability discovery, and exploitation research.
  • Kept human review and evidence checks between stages.
  • Prompted research workflows with explicit validation gates.
  • Supported a more structured way to evaluate assisted security research.
offensive-securityai-security

Tech Stack

Security Controls

Operational security work tied to control behavior.

Autonomous Operations

Repeatable, evidence-grounded workflows for security operations.

Endpoint & Detection

Endpoint evidence and maintainable detection work.

AI/LLM Workflows

Evidence-grounded assistance with human validation gates.

Offensive Validation

Research across reconnaissance, vulnerability discovery, and exploitation.

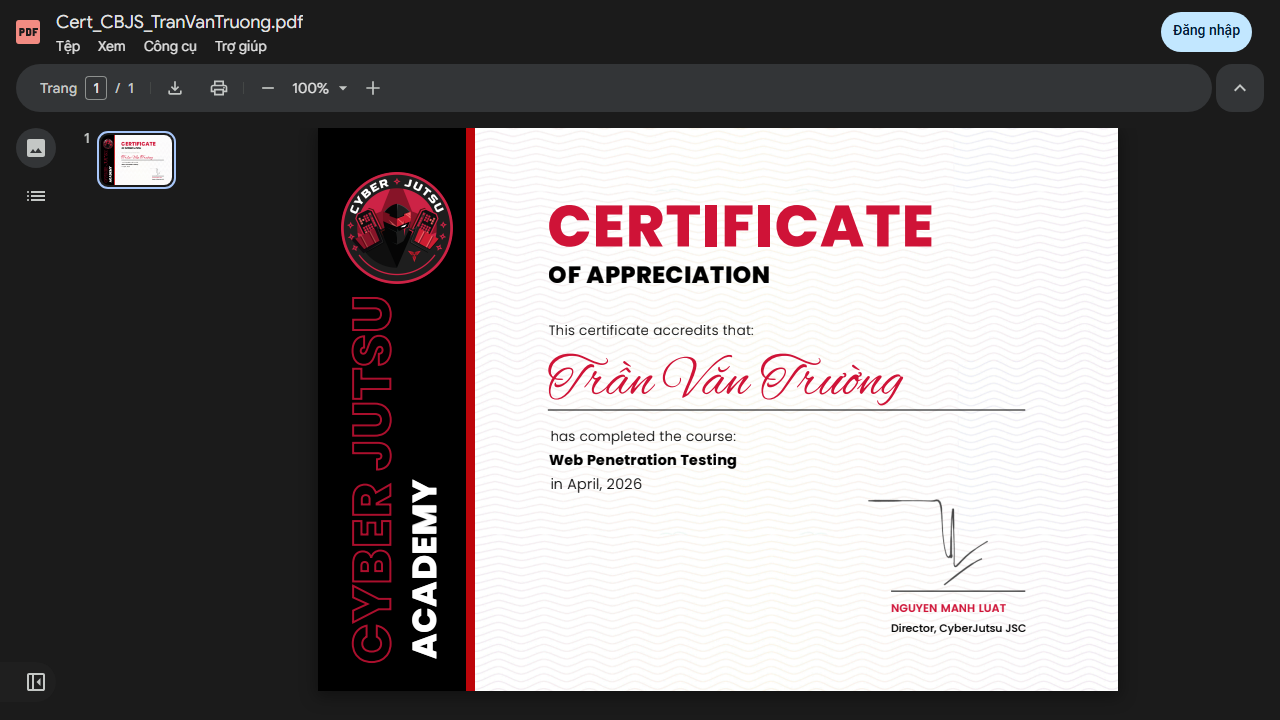
Credentials

Computer and Information Systems Security/Information Assurance

University of Information Technology

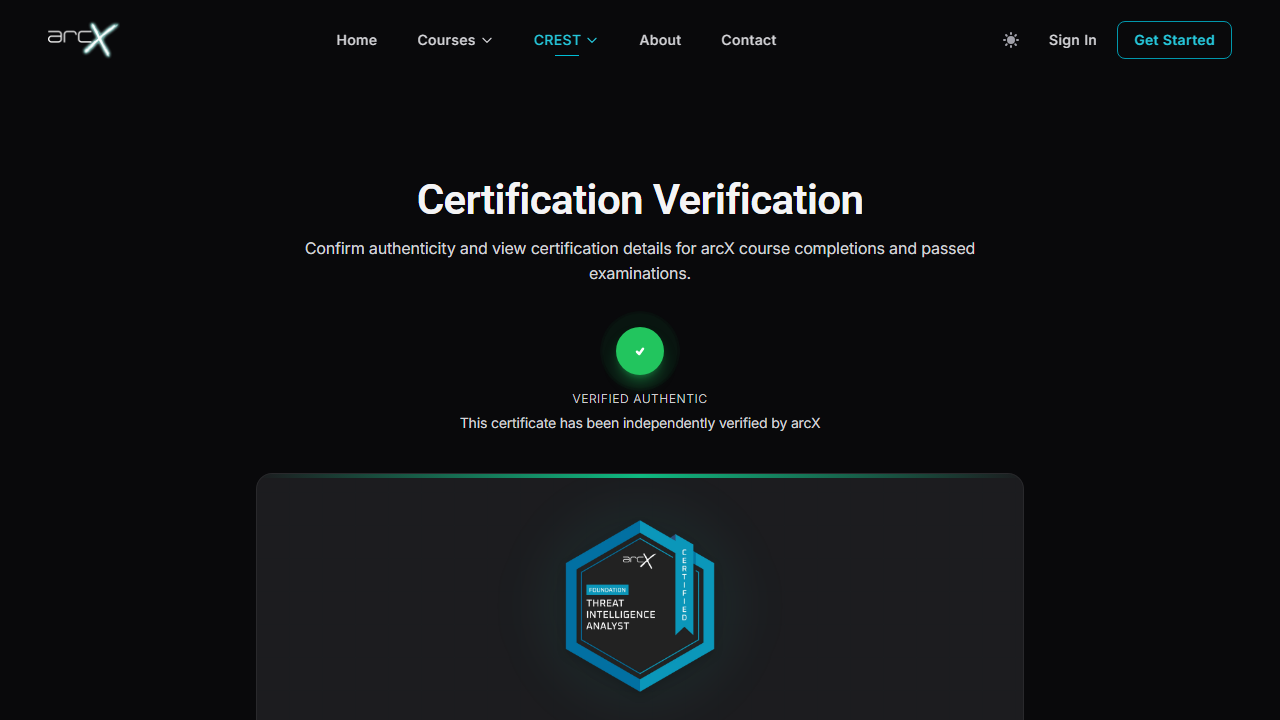
Foundation Level Threat Intelligence Analyst

arcX

395446bfd6488c1bd913ca850bc388df7a52487dVerify credential

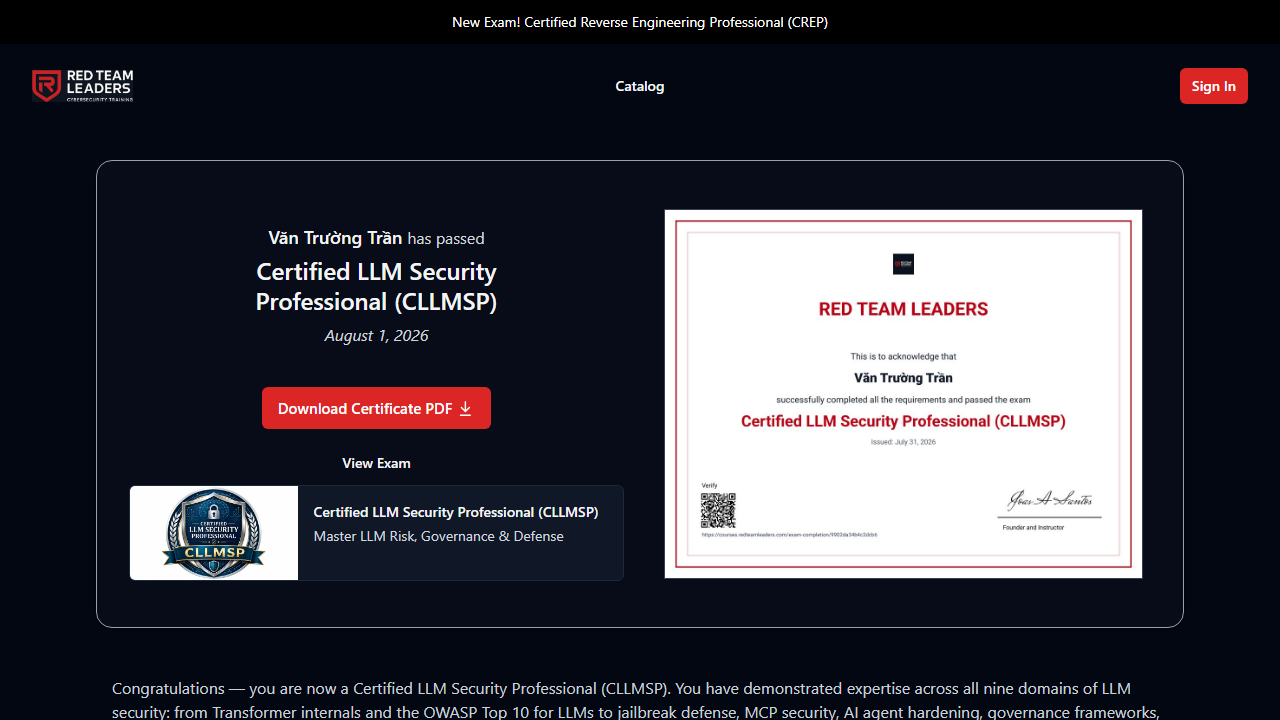
Certified LLM Security Professional (CLLMSP)

Red Team Leaders

Ask My Portfolio

The portfolio assistant is not configured. These suggestions remain available as browsing prompts.

Example questions

  • How does Van's Autonomous SecOps approach combine AI reasoning with human approval?
  • What security controls and continuous validation experience does Van have?
  • Which relevant Information Security experience supports Van's Autonomous SecOps work?
  • How has Van used evidence-grounded AI in security workflows?
  • What work arrangements is Van open to?
  • How can I contact Van?

Contact

Get in touch about security operations roles or relevant international freelance work.

Onsite or hybrid full-time in Vietnam; remote for relevant international freelance work.

Ho Chi Minh City, Vietnam

truongvtrpaul@gmail.comGitHubLinkedIn